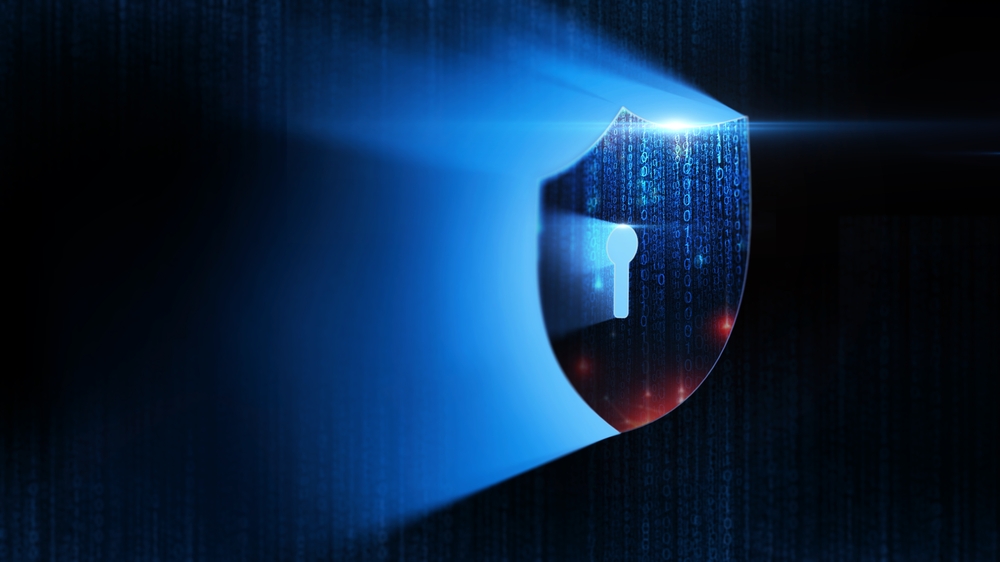
Victor Mateu, Chief Researcher of the Cryptography Research Center at the Technology Innovation Institute (TII), explains why the risks posed by quantum computing demand attention today, and how organisations can prepare for the transition to quantum-safe security.
Give an overview of the work being done at TII’s Cryptography Research Centre and your current priorities?
TII is a research institution with multiple research centres covering areas such as robotics, autonomous systems, AI, and cryptography, which is the centre I lead.
In cryptography, we develop the cryptographic primitives that underpin other security solutions. Banking applications, for example, rely on cryptography for encryption, authentication, and secure communications.
Our focus is on developing the next generation of these technologies, including post-quantum cryptography, which is designed to protect against attacks from quantum computers.
We are also looking at AI, particularly the protection of inference. We already have cryptography to secure communications, but AI introduces new considerations around how data is processed. We are sharing significant amounts of information with AI systems, and that data needs protection, both for users interacting with models and those whose data is used for training. Our research aims to provide privacy on both sides.
Quantum computing is still largely seen as a technology of the future. Why should organisations already be prioritising quantum security?
The main concern is how long information needs to remain confidential.
A private communication accessed several months later can still represent a serious privacy violation because the information may retain its value. When we consider government information or corporate intellectual property, that information may need protection for decades.
The concern is that a sufficiently powerful quantum computer could become available within that period.
We are only beginning the transition to post-quantum cryptography, and many organisations do not even have a complete understanding of the cryptographic systems deployed across their infrastructure.
If a capable quantum computer becomes available in 10 years, we could already be too late. Communications happening today can be intercepted and stored, then decrypted when the technology becomes available.
There is a perception that the threat begins when the quantum computer arrives. In reality, the risk already exists because information can remain sensitive long after it has been transmitted.
I believe that if we don’t have sufficiently capable quantum computers within the next decade, it will be surprising.
How close are we to that capability, and where do you see the most significant security vulnerabilities?
Progress is happening on two fronts. Quantum computers are becoming more capable, while quantum algorithms that could break existing cryptographic systems are becoming increasingly efficient.
We have better computers tackling problems that require fewer resources. Eventually, these developments will converge.
There is also significant investment in quantum technologies, with governments supporting companies developing these capabilities. In the UAE, TII has developed its own quantum computer. It is relatively small, but its components and design were developed locally.
In terms of vulnerabilities, I see two major threats.
The first concerns communications being harvested today for decryption later. Whether that capability arrives in 10 or 11 years is difficult to predict. The important point is that certain cryptographic algorithms will become vulnerable, so organisations should begin transitioning as soon as possible.
The second concerns the root of trust embedded in hardware.
Devices rely on cryptographic signatures to establish trust. But consider infrastructure designed to operate for decades, such as cash machines or satellites. Their security may depend on classical cryptography embedded directly into hardware.
Once those algorithms become vulnerable, attackers could potentially compromise systems that rely on them.
Software-based security can often be updated, but when the root of trust is embedded in hardware, replacing those cryptographic protections becomes much more complicated. For me, this represents a significant long-term risk.
What does quantum readiness look like in practice, and where should organisations begin?
It comes down to understanding your existing infrastructure. There is a fundamental principle in cybersecurity: you cannot protect what you don’t see.
Organisations need mechanisms to discover the cryptography deployed across their infrastructure and classify which systems are quantum-safe and which require updates.
That provides the basis for a gap analysis, followed by migration planning.
For me, the immediate priority is cryptographic discovery. If organisations complete that process thoroughly, they will be in a much stronger position for the next stages.
By the end of 2026, organisations should be ready to conduct a gap analysis, and by mid-2027, they should have a migration plan.
Migration will take time, but it cannot be executed properly without understanding the existing environment. Otherwise, an organisation could complete a migration and still remain exposed because critical systems were overlooked.
Ultimately, security should remain seamless for users. Cryptography is already embedded in everyday applications, from mobile devices to banking transactions. The next generation of security solutions should work in much the same way.
The best security is the security you don’t see.
Finally, how does TII’s research across cryptography, quantum computing, and AI support the development of quantum-safe security?
TII has a privileged position because we have research centres working across these disciplines.
We have visibility into the threat through our quantum research and, at the same time, an understanding of how to protect against it through cryptography.
Our researchers can examine potential attacks and discuss their feasibility directly with colleagues developing quantum technologies. Similarly, we can ask them to evaluate whether the cryptographic solutions we are developing could be broken.
Sometimes they disprove an attack. Sometimes they identify something requiring closer attention. This collaboration helps us strengthen our security research.
AI also connects with both cybersecurity and quantum computing. These areas are interconnected, and having that expertise within one institution creates significant opportunities to advance research and develop stronger security technologies.

Discussion about this post