• About Us
  • Advertising
  • Digital Magazine
  • Supplements
  • Media Pack
  • Privacy Policy
  • Contact us
CXO Insight Middle East
  • News
  • Opinion
  • Business
    • Industries
      • Transport
      • Retail
      • Government
      • Real Estate
      • Education
      • Energy
      • Banking and Finance
    • Channel
  • Future
    • Tech
    • Gadgets
    • Science
    • Space
    • Sustainability
  • Events
    • Channel Awards
      • 2025
      • 2024
      • 2023
    • Channel Insights Summit
      • 2026
      • 2025
    • Webinars
      • AI in Finance
      • The Resilient Enterprise
    • CXO50 KSA
    • CXO50 Oman
    • CXO50
      • 2026
      • 2025
    • ICT Awards
      • Dubai 2025
      • Saudi Arabia
    • Cyber Strategists Summit
      • 2026
      • 2025
      • 2024
      • 2023
      • 2022
      • 2021
    • Cloud Connect 2025
    • All events
  • Digital Magazine
  • GITEX x AI EVERYTHING
No Result
View All Result
CXO Insight Middle East
  • News
  • Opinion
  • Business
    • Industries
      • Transport
      • Retail
      • Government
      • Real Estate
      • Education
      • Energy
      • Banking and Finance
    • Channel
  • Future
    • Tech
    • Gadgets
    • Science
    • Space
    • Sustainability
  • Events
    • Channel Awards
      • 2025
      • 2024
      • 2023
    • Channel Insights Summit
      • 2026
      • 2025
    • Webinars
      • AI in Finance
      • The Resilient Enterprise
    • CXO50 KSA
    • CXO50 Oman
    • CXO50
      • 2026
      • 2025
    • ICT Awards
      • Dubai 2025
      • Saudi Arabia
    • Cyber Strategists Summit
      • 2026
      • 2025
      • 2024
      • 2023
      • 2022
      • 2021
    • Cloud Connect 2025
    • All events
  • Digital Magazine
  • GITEX x AI EVERYTHING
No Result
View All Result
CXO Insight Middle East
No Result
View All Result

Orchestration and Threat Intelligence – Engine and Fuel

by CXO Staff
December 16, 2020
in Opinions

Anthony Perridge says the orchestration tool is about working the reflex, while the threat intelligence practice is about working the memory.

threat intelligence
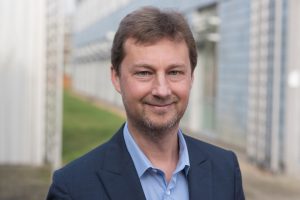
Anthony Perridge, ThreatQuotient

These days we believe that “it’s not a matter of if, but when and how” we’ll be attacked. So, we’ve expanded our focus from prevention to include detection and response, and organisations are talking about using Security Orchestration, Automation and Response (SOAR) tools.

According to Gartner’s Market Guide for Security Orchestration, Automation and Response (SOAR) Solutions, by year-end 2022, 30% of organisations with a security team larger than five people will leverage SOAR tools in their security operations, up from less than 5% in 2019. There are many factors driving demand, chief among them the shortage of skilled cybersecurity talent which is compelling most organisations to look for ways to automate routine, repeatable tasks.

Orchestration tools, specifically playbooks, are good for automating processes that we know we always perform the same way. The system responds reflexively, thus reducing the need for humans in this capacity. Playbooks help Incident Response (IR) teams accelerate response and mitigate risk, while freeing up expert resources to focus on higher value tasks which also helps with employee retention.

An organisation’s Threat Intelligence practice has a different role – gathering external and internal threat and event data, normalising it for analysis, and automatically scoring and prioritising it based on organisation-specific parameters. With a platform that serves as a central repository and organisational memory, teams and tools have access to the organisation’s history of investigations, observations and learnings about adversaries and their tactics, techniques and procedures (TTPs). Adding new data and learnings over time, the platform automatically reevaluates and reprioritises intelligence to support ongoing detection, investigation and response.

Both orchestration tools and a threat intelligence platform serve the same high-level goal: Optimise people’s time so they can focus on areas where their intelligence, experience and skills are needed, and don’t waste time on things that can be easily automated. What makes these tools even stronger is when they work together.

The fact is, there is more we can do to optimise playbooks so that they save exponentially more time. When driven by threat intelligence, an orchestration tool can recognise connections and patterns, and adjust playbook runs to maximise efficiency. And when a threat intelligence platform brings in learnings from the IR practice, it can augment and enrich threat intelligence with greater context to further accelerate detection and response.

Using a phishing campaign as an example, let’s say that the organisation has been targeted with 100 emails. The playbook flags something unknown, forwards it to a tool for inspection which confirms it is suspicious, then sends it to a sandbox that validates it is malware. The file is then added to the reputation block list. When the next suspicious email comes in, the playbook repeats the same process. Over time the reputation list gets longer and longer, and system performance gets slower and slower responding repeatedly to the same requests.

But if the orchestration tool works in concert with the threat intelligence solution, then the full playbook does not need to be executed each time. The threat intelligence platform remembers activity from the same malware family and campaign and recognises that it is an immediate and actual threat to the organisation and scores it accordingly at a 9 or 10. The playbook can be written to adjust processes based on scoring so, for example, a score of 7-10 may trigger automatic blocking. A score of 3 to 7 may send the file directly to the sandbox. Anything lower initiates the full playbook. The ability for playbooks to dynamically adjust based on scoring increases the efficiency of tools and teams.

Another aspect that improves when orchestration and threat intelligence work together, is reputation list management. It isn’t the job of the orchestration tool to curate the reputation list which can become unwieldy very quickly. However, a threat intelligence platform tracks and stores threat and event data from all sources and groups and remembers what it has seen, which allows it to understand the lifecycle of the threat and when to cull the reputation list. Because information that is no longer relevant is removed, new information can be added without the risk of overloading the reputation list.

The orchestration tool is about working the reflex, while the threat intelligence practice is about working the memory. Although their approaches are different, orchestration tools and threat intelligence platforms share the same goal: to accelerate detection, response and risk mitigation. And when they work together, they save teams more time and deliver even better results.
Tags: Anthony Perridgefeatured4orchestration toolThreat IntelligenceThreatQuotient
ShareTweet

Related Posts

Building for AI: The changing economics of data centre power
Brand View

Building for AI: The changing economics of data centre power

September 7, 2026

The rapid expansion of AI infrastructure is forcing data centre operators to revisit assumptions that have shaped power design for...

Why talent is becoming the most important AI investment
Opinions

Why talent is becoming the most important AI investment

August 27, 2026

The organisations creating the greatest value from artificial intelligence are not necessarily those spending the most on AI. They are...

Discussion about this post

Latest Issue

Cisco expands Secure AI Factory with NVIDIA for the rack-scale era

Cisco expands Secure AI Factory with NVIDIA for the rack-scale era

September 8, 2026
Pieter Bil joins GBM as Chief Executive Officer

Pieter Bil joins GBM as Chief Executive Officer

September 8, 2026
Saviynt appoints Kamel Heus as VP Sales for the MEA

Saviynt appoints Kamel Heus as VP Sales for the MEA

September 8, 2026

The most trusted source of strategic intelligence for IT decision makers in the Middle East.

About

  • About Us
  • Advertising
  • Digital Magazine
  • Supplements
  • Media Pack
  • Contact Us

Policies

  • Privacy Policy
© 2025 – CXO Insight Middle East. All Rights Reserved.
Facebook-f X-twitter Linkedin
Separated they live in Bookmarksgrove right at the coast of the Semantics, a large language ocean. A small river named Duden.

About

  • About Us
  • Site Map
  • Contact Us
  • Career

Policies

  • Help Center
  • Privacy Policy
  • Cookie Setting
  • Term Of Use

Join Our Newsletter

© 2024 – CXO Insight Middle East. All Rights Reserved.

Facebook-f Twitter Youtube Instagram

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In
Join our mailing list
Sign up here to get the latest news, updates and special offers delivered directly to your inbox.
No Result
View All Result
  • News
  • Opinions
  • Business
    • Industries
      • Transport
      • Retail
      • Government
      • Real Estate
      • Education
      • Energy
      • Banking and Finance
  • Channel
  • Future
    • Tech
    • Gadgets
    • Science
    • Space
    • Sustainability
  • Events
    • Channel Awards
      • 2025
      • 2024
      • 2023
    • Channel Insights Summit
      • 2026
      • 2025
    • Webinars
      • AI in Finance
      • The Resilient Enterprise
    • CXO50 KSA
    • CX50 Oman
    • CXO50
      • 2026
      • 2025
    • ICT Awards
      • Dubai
      • Saudi Arabia
    • Cyber Strategists Summit
      • 2026
      • 2025
      • 2024
      • 2023
      • 2022
      • 2021
    • Cloud Connect 2025
    • All events
  • Videos
  • GITEX x AI Everything
  • Digital Magazine

© 2025 - CXO Insight Middle East. All Rights Reserved.